HackTheBox Certified Defensive Security Analyst (CDSA) Exam Review
Context
My experience with CDSA, thoughts, and whatnot.
Since I enjoyed blue teaming much more than red teaming, I wanted to take a cheap cert. CDSA is exactly that. Just because it is cheap, doesn’t mean it is low quality. I’ve came across HackTheBox’s CDSA cert. It’s slightly different than my internship in DFIR in the sense that it’s a SOC analyst level, but still alligns with blue teaming. I decided to study and obtain this cert. Why though? It’s not HR recognised, you won’t come across this as a filter through jobs unlike Security+ or CySA+. Well, I took it because it provides MUCH better hands on technical skills for working in a SOC environment. Plus, HTB certs are well respected in the community imo, so why not.
HackTheBox CDSA Modules
I feel like the SOC Analyst (https://academy.hackthebox.com/app/paths/390) academy modules is EXTREMELY important when it comes to preparing you. It gives you the tools, you just need to use it in the exam. throughout my study process, I basically just copy pasted the texts, chuck them into Obsidian, and I summarise them in my head. I feel like I could at least type my own summary with --- below the blob of text. But I didn’t (I already took the test, now for future modules, I will be implementing that). Overall the 15 modules took me about 4 months to complete (I was stuck on the Windows Attack and Defense module for a 2-3 weeks, trying to wrap my head around it). It was also the time period when I took my 2 week-long uni break.
Exam prep
My exam prep is reading through my notes in the airplane, bus, downtime, etc. It helps with not doing anything during the holiday. I don’t think this helps too much though, so I would skip. I also did the CDSA prep path: https://app.hackthebox.com/tracks/79 I feel like it’s such a great way of getting back from the holiday. I didn’t do all of them ofc. I only did 1 of each category:
| Category | Box name |
|---|---|
| Very Easy | Campfire-1 |
| Easy | Trojan |
| Medium | ReliableThreat |
| Hard | Streamer |
Please note that HackTheBox VIP+ subscription is required to complete those sherlocks.
Among all of them, I only practiced report writing a report on Campfire-1. I screenshot IOCs, build a timeline from start, etc.
I also did the Splunk BOTSv1 (Boss Of The Splunk). As I have been reading about people finding it helpful prep before the exam. https://bots.splunk.com/event/3oQ7sqI5bajOCP43o0svqT/detail
I also read a bunch of DFIR report. thedfirreport.com is also a great read. It makes you understand how an attacker thinks and how the DFIR responds to incidents. Since HTB CDSA requires you to submit a commercial grade report.
The Exam
Once I felt ready, I clicked the scary Enter Exam button on Friday. I got met with the exam’s T&Cs and I was like:
So I just scrolled all the way and clicked agree. Since I can’t really talk about the actual exam, this meme sums up the exam for me:
Yes. I felt like I had to devote my life for 7 straight days. Those 7 days were fun, though gruelling. I feel like the exam has very realistic attack path, and real life threat actors would possibly use the attack path.
I personally found 12/20 flags in the first day, up to 18/20 flags on 2nd, and all 20/20 on the third. It took me 2 days to write a report on that. I was definitely aware that report will take more time than finding flags and I was dedicating 12+ hours per day. My first flag was quite hard in terms of admin as I forgot to refresh the exam panel before submitting the flag. so, please don’t make the same mistake lol.
The rest of the flags sort of guided me as a “hint” (these flags are HARD, trust me). I forgot how to use some tools, so I revisit some modules and that was pretty much my strategy. I feel like 7 days are at the sweet spot for this exam as there’s enough time to write up 2 incidents, and not too much days for slacking off (even if it’s not, there’s 2nd attempt). I also find it that if I’m lost on a flag, I can just skip and go to the next one. Because you WILL find the answer for that flag later. None of the flags are impossible or too hard once I understood the main idea of those incidents.
Note-Taking & Reporting
Note Taking
There’s heaps of note taking apps available, but I personally use Obsidian. I map IoCs and construct timeline as I go. Understanding every command or queries that was provided in the path is a must. Copy pasting won’t help in the exam.
So for example, calculator.exe spawns cmd.exe then you should know which place to look for, how to find which user executed that, what event IDs to focus, how to discover even more information about this incident.
Take as much screenshots as you go, and paste the SIEM query above it. That’s definitely going to help with report writing (trust me, I started doing this too late)
Reporting
Ahh yes, my favourite part is report writing!
The main options for report writing is:
- Word Template
- Sysreptor
Word template is provided during the exam, but I personally use Sysreptor. The SOC analyst path also did a whole module about report writing, so my report’s template is similar to that. The UI is friendly and it looks quite well made, so I used that for the whole duration of the exam. For reporting, the advice is to make a timeline first, store it in your notes, and then build the report alongside it. The template I used it:
Time:
Activity: What the attacker did
Method: (Evidence or pictures supporting the activity)
Queries: Any SIEM or tools output that are relevant
Explanation: Explaining why it's malicious or suspicious
Those are just rough templates, I would’ve prepared something like this before reporting, then start reporting. This would’ve saved me a lot of time because I can easily chain my findings.
After the Exam
It’s done. Flags are collected, report have been submitted. Now what?
Well I think I did miss some key points in the exam, and I don’t know why I just blanked and submitted my exam so quickly. My genuine reaction to that was:
And yes, I did went through the 5 stages of grief lol.
Results
It was 10 pm today (2026-09-22) that I got the email that I passed and that I’m a “certified hacker”. I was definitely relieved. After all the hard work, sherlocks practiced.
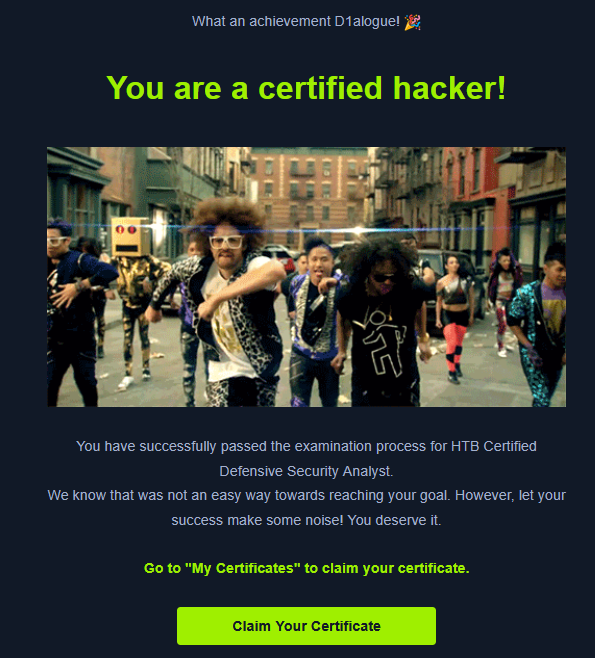
This was definitely one of the hardest, most gruelling exam I had to take. And I’m glad I can finish and pass it.
The badge can be viewed here:
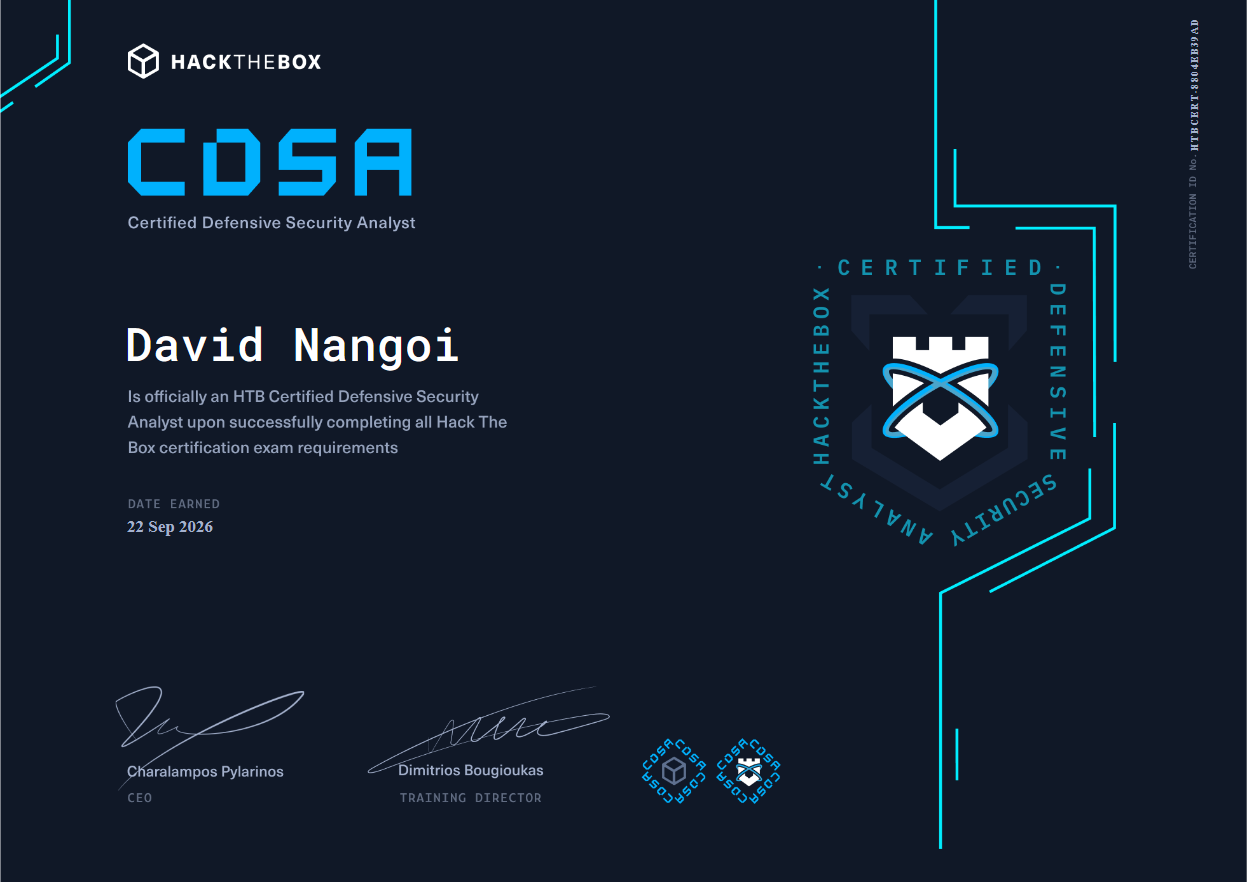
Here’s my certificate:
What’s next?
I’m not too sure on what to pursue yet, there are no set targets. Since I’m still studying at the time of writing this, I’m going to finish my honours project and see where I go from there. I’m currently in the middle of doing CPTS and are trying to explore my options in purple teaming (my passion still lies in the blue teaming side of things though). I heard that CyberDefenders CCD are pretty good, mainly the CCDL2. But, we shall see what I pursue next, because: